
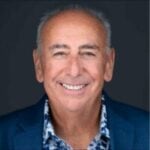
 Alan Shimel is founder, CEO and editor-in-chief of Techstrong Group, a Futurum company, and a member of Futurum's executive leadership team. A technology entrepreneur, media executive and industry commentator, Shimel has spent more than three decades building businesses, communities and media platforms serving enterprise technology professionals, including co-founding StillSecure, a network security company, and the DevOps Institute, a DevOps certification and training body. At Techstrong, he leads a portfolio of media brands including DevOps.com, Security Boulevard, Cloud Native Now, Techstrong AI, Techstrong IT, Digital CxO, Platform Engineering, Techstrong Semi and Techstrong TV, along with a growing portfolio of events, educational programs and digital communities. With more than 25 years of experience in cybersecurity, Shimel is a familiar voice in the space and was an early advocate of the DevOps movement, helping bring DevOps practices into mainstream enterprise technology. His work today spans cybersecurity, DevOps, cloud-native technologies, artificial intelligence, semiconductors and digital transformation, and he hosts popular programs including Techstrong Gang, Shimmy Says and Still Cyber, After All These Years. He holds a Bachelor of Arts in Government and Politics from St. John's University and a Juris Doctor from New York Law School.
LLMs & Kubernetes Configuration: Automating Hardening, Drift Detection and Policy Enforcement
Kubernetes misconfigurations remain the top security risk. AI copilots promise automated hardening, drift detection, and policy enforcement to make clusters safer ...
Service Mesh Evolution: Ambient Mode, Gateways & The Return of Simpler Architectures
Service mesh is evolving beyond sidecars. Ambient mode and Gateway APIs deliver security, observability, and traffic control with less overhead. Teams benefit from leaner, more flexible architectures ...
Stateful Microservice Migration & the Live-State Challenge in Kubernetes
Alan argues that Kubernetes can’t ignore state any longer. While stateless apps fit the original vision, real-world workloads — from databases to AI pipelines — demand continuity. A new research framework, MS2M ...
Bridging Observability & Security in Kubernetes: Beyond Just Metrics
Kubernetes has expanded agility but also the attack surface. Alan argues that observability and security can no longer live in silos — metrics, logs, and traces already hold critical security signals, while ...
GitOps at Fleet Scale: Decentralization vs. Control
Alan unpacks Red Hat’s agent-based GitOps architecture for OpenShift and what it means for scaling GitOps across fleets of Kubernetes clusters. From central control to decentralized agents, discover how balance drives the ...
CNCF and Docker: The Next Phase of Cloud Native Supply Chain Evolution
The CNCF–Docker partnership strengthens cloud native supply chain security with verified namespaces, SBOMs, and signed images. Trust becomes the new baseline ...
The Cloud-Native Frontier is at the Edge
The future of cloud-native is hybrid and edge. Learn how WebAssembly (WASM) complements containers to power next-gen workloads with speed, security and agility ...
OpenTofu and the New Era of Infrastructure as Code
Terraform’s license shift sparked OpenTofu’s rise. Alan explores how IaC now thrives with both HashiCorp’s Terraform and CNCF’s OpenTofu shaping the future ...
Supply Chain Security: Cloud Native’s Weakest Link?
For years, the conversation in security revolved around networks, firewalls, and endpoints. The perimeter was king. But in the cloud-native era, the old perimeter has dissolved into microservices, APIs, and pipelines. What’s ...
Runtime Visibility: The Missing Layer in Cloud-Native Security
Cloud-native security can’t rely on old perimeter defenses. With workloads spinning up in seconds, runtime visibility is now the missing layer leaders must prioritize. Learn why observability is security, how tools like ...

